

<p>Fundamental flaws in the encryption system used by popular solid-state drives (SSDs) can be exploited by miscreants to easily decrypt data. ;</p>


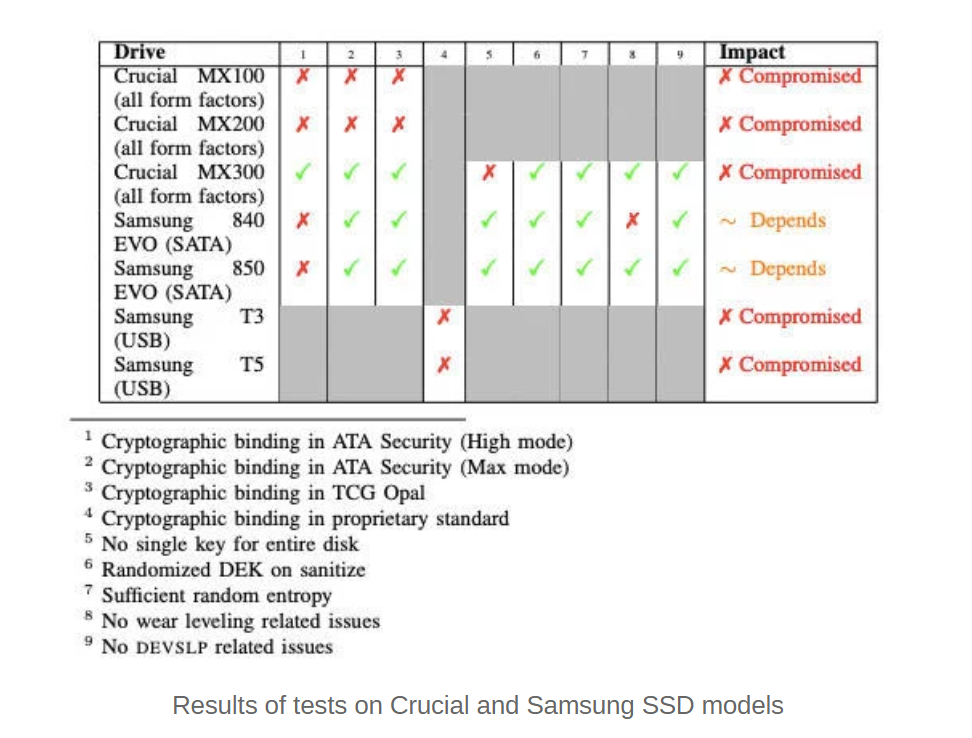
<p><br>&#8220;The analysis uncovers a pattern of critical issues across vendors,&#8221; according to the researchers. &#8220;For multiple models, it is possible to bypass the encryption entirely, allowing for a complete recovery of the data without any knowledge of passwords or keys.&#8221;</p>


<p>A ;<a target="_blank" rel="noreferrer noopener" href="https://t.co/UGTsvnFv9Y">paper</a> ;[PDF] drawn up by researchers Carlo Meijer and Bernard van Gastel at Radboud University in the Netherlands, and made public today, describes these critical weaknesses. The bottom line is: the drives require a password to encrypt and decrypt their contents, however this password can be bypassed, allowing crooks and snoops to access ciphered data.</p>


<p>Researchers could retrieve the keys by modifying the drive&#8217;s firmware, or by exploiting a code injection vulnerability that would also allow an attacker to modify the password routine – both require physical access to the drive.</p>


<figure class="wp-block-image"><img src="http://www.thecloudxperts.co.uk/wp-content/uploads/2018/11/image.png" alt="" class="wp-image-345"/></figure>


<p>

Unfortunately, the pair also note that some popular data encryption systems, including the BitLocker tool Microsoft uses in Windows 10, do not use software encryption for SSDs and rely on the drive&#8217;s vulnerable hardware encryption.

</p>


<p><strong>Microsoft advisory is to switch to software encryption to mitigate risk</strong></p>


<h2 class="wp-block-heading"><strong>Check your Drive Encryption Status ;</strong></h2>


<p>To check the type of drive encryption being used (hardware or software):</p>


<ol class="wp-block-list"><li>Run ‘manage-bde.exe -status’ from an elevated command prompt.</li><li class="">If none of the drives listed report “Hardware Encryption” for the ;<strong>Encryption Method</strong> ;field, then this device is using software encryption and is not affected by vulnerabilities associated with self-encrypting drive encryption.</li></ol>


<h2 class="wp-block-heading">Switch to Software Encryptions</h2>


<p>Microsoft Advisory: For drives that are encrypted using a vulnerable form of hardware encryption, you can mitigate the vulnerability by switching to software encryption using <g class="gr_ gr_3 gr-alert gr_spell gr_inline_cards gr_run_anim ContextualSpelling ins-del multiReplace" id="3" data-gr-id="3">Bitlocker</g> with a Group Policy.</p>


<pre class="wp-block-preformatted"><strong>Note</strong>: After a drive has been encrypted using hardware encryption, switching to software encryption on that drive will require that the drive be unencrypted first and then re-encrypted using software encryption. If you are using BitLocker Drive Encryption, changing the Group Policy value to enforce software encryption alone is not sufficient to re-encrypt existing data.<br></pre>


<p><strong>To mitigate vulnerabilities associated with self-encrypting drives on Windows systems:</strong></p>


<ol class="wp-block-list"><li>Configure and deploy a Group Policy to enable forced software encryption.</li><li>Fully turn off BitLocker to decrypt the drive.</li><li>Enable BitLocker again.</li></ol>


<h2 class="wp-block-heading"><strong>Use Intune to Force settings ;</strong></h2>


<ol class="wp-block-list"><li>Get the GPO key HKLM:\SOFTWARE\Policies\Microsoft\FVE<br>FDVHardwareEncryption = 0 (dword)</li><li>Use Intune PowerShell to apply the setting</li></ol>


<h2 class="wp-block-heading">BitLocker Policy Settings for software-based encryption</h2>


<p>

This policy setting allows you to manage BitLocker&#8217;s use of hardware-based encryption on fixed data drives and specify which encryption algorithms it can use with hardware-based encryption.

</p>


<table class="wp-block-table"><tbody><tr><td>Registry ;Hive</td><td>HKEY_LOCAL_MACHINE</td></tr><tr><td>Registry ;Path</td><td>SOFTWARE\Policies\Microsoft\FVE</td></tr><tr><td>Value ;Name</td><td>FDVHardwareEncryption</td></tr><tr><td>Value ;Type</td><td>REG_DWORD</td></tr><tr><td>Enabled ;Value</td><td>1</td></tr><tr><td>Disabled ;Value</td><td>0</td></tr></tbody></table>


<p><strong> Use BitLocker software-based encryption when hardware encryption is not availabl</strong>e, You can allow failover <br></p>


<p><strong> ;Restrict encryption algorithms and cipher suites allowed for hardware-based encryptio</strong>n<br></p>


<p><strong>Restrict crypto algorithms or cipher suites to the following: ;</strong><br></p>


<pre class="wp-block-verse"><strong>Reference:<br></strong>https://portal.msrc.microsoft.com/en-us/security-guidance/advisory/ADV180028<br>https://forums.theregister.co.uk/forum/1/2018/11/05/busted_ssd_encryption/</pre>